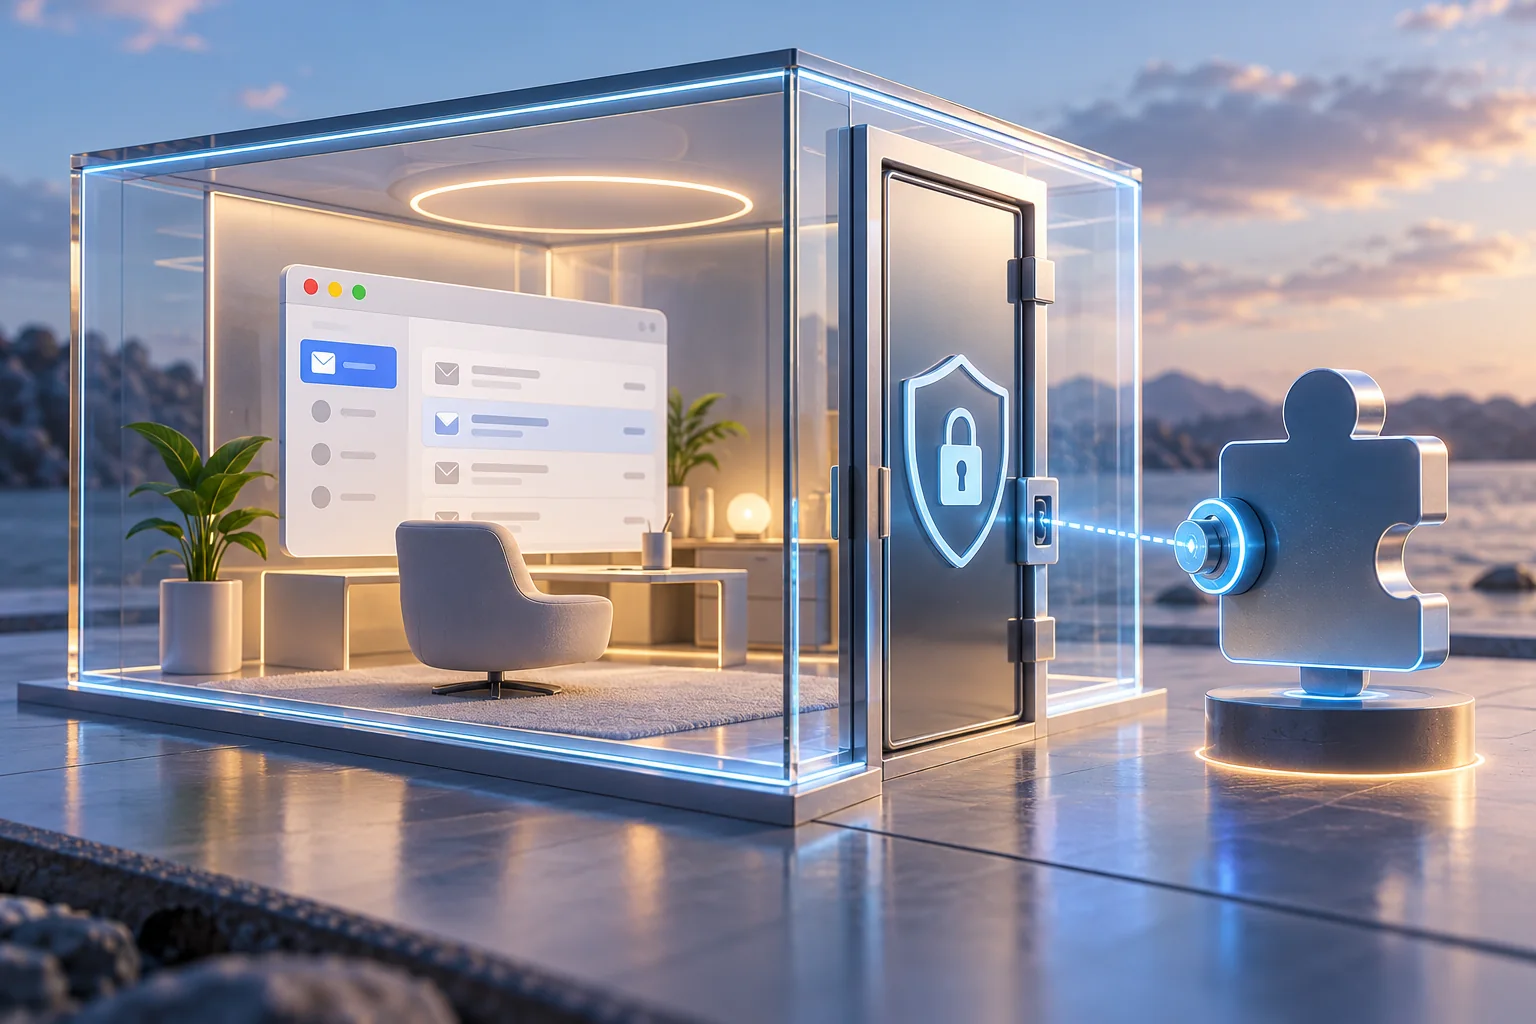
When evaluating a private phone number to receive SMS, turn private into a set of specific access questions. It may describe an exclusively allocated number, a login-protected inbox, or a particular sharing arrangement. Those meanings are related, but they are not interchangeable.
A useful review asks who can use the number, who can read its messages, which copies can leave the inbox and what happens when access ends. Product names alone cannot supply those answers.
Allocation is only one boundary
An exclusively allocated number may prevent other customers from using it during the agreed period. That does not explain which people can enter the account that manages it. If a whole team shares one login, the practical audience for incoming messages includes everyone who holds that credential.
Ask whether individual users can be authorized separately, if that feature matters to the task. For personal use, check how the inbox account is recovered and whether recovery relies on a number or email address you still control. A private inbox is not very useful if its own recovery path is inaccessible.
Do not interpret exclusive allocation as proof that the number has never had another user. Unless the provider makes that claim explicitly, treat unfamiliar incoming messages as potentially unrelated. Never use a code or recovery link to access an account that is not yours.
Find every place the message can appear
The browser view may be only one destination. Depending on the product, notifications, email forwarding, downloads or an application integration can create additional copies. Ask which of those features are enabled and who can access the destinations. A carefully protected dashboard can be undermined by forwarding every message to a widely shared mailbox.
Check whether notifications display message contents on a shared device. If the service provides a way to reduce that exposure, consider it for sensitive communications. The exact options depend on the product; do not assume that a hidden browser tab also hides notifications or downloaded files.
Retention needs a separate answer. Deleting a text from the visible list does not establish what happens to exported copies or provider-held records. Review the applicable retention statement and distinguish a user's delete action from a promise about every remaining copy.
Match access to the actual job
For general business replies, several authorized people may legitimately need access. For a personal sign-in code, a shared operational inbox may be a poor fit even if the number itself is dedicated. Decide based on message sensitivity and ownership, not on whether collaboration features sound convenient.
If someone is helping troubleshoot a missing message, give the smallest useful evidence: an approximate time, the affected number as necessary, and the observed error. Avoid sending live codes, full account details or screenshots of neighboring messages. Support coordination does not require turning an entire inbox into a shared attachment.
An effective check can be written as four short statements: the number is allocated under understood conditions; only authorized people can enter the inbox; forwarding and downloads have known destinations; and there is a clear exit procedure. If one statement remains uncertain, record it as an open question rather than assuming privacy.
For team evaluation, include an ordinary access-change exercise in the review. Ask how an authorized member would be removed and how the remaining team would continue working. Check whether existing sessions and forwarding destinations need separate attention. Do not label a product secure merely because changing a password is possible; establish which access paths that change actually affects.
For personal evaluation, consider the same issue with devices rather than staff. If an old computer is no longer under your control, determine which documented session controls are available from a trusted device. These questions do not require a live verification code or a real account-recovery attempt. They help establish the practical boundary around the inbox before confidential content is placed inside it. Where a control is unavailable, record that limitation instead of inventing a replacement feature.
When you stop using the service, remove account dependencies through the relevant platforms and follow the provider's process for closing access. Privacy is a property of the whole arrangement, including the end of its use. It cannot be established solely by seeing a password field or the word private on an order page.
Review the indirect views as well as the inbox
Where a service offers forwarding, search, exports or notification previews, check who can use each feature. A restricted detail page does not establish that every secondary copy has the same audience. Do not assume those features exist; list only the ones the product actually provides.
For a team, test the authorized roles separately and remove temporary access afterwards. If the only available arrangement is one shared login, record that limitation rather than describing it as individual, accountable access.